
Information Security
Approach and Policy
Basic NGK Group Information Security Policy
As our information-communication society grows ever more sophisticated, the NGK Group has come to handle much more in the way of information assets, and is aggressively pursuing the safekeeping of any and all information assets it retains. While it is essential to share these assets in order to conduct business in a smooth and efficient manner, establishing a system for information security likewise becomes a necessity. For this reason, the NGK Group has set forth this basic policy regarding information security and will work to safeguard the information assets in its possession.
- In order to ensure the safety of retained information assets, which includes information retained in the course of business activities, as well as any devices, facilities, or services necessary to handle said information, we will establish an information security management system to prevent unauthorized intrusion, loss, theft, leaks, modification, damage, denial-of-service attacks, and any other threat.
- All individuals who work at any office of NGK or its group companies and who make use of information assets will be subject to ongoing information security education and training for an increased awareness of security issues. Actions in violation of this Policy may be subject to legal penalties, as well as reprimands set forth in labor regulations, contracts, and/or other binding documents.
- Should a security issue arise concerning information assets, we will promptly investigate the cause and work to keep any damage to a minimum.
- We will comply with all laws and social norms with regard to information security, as well as any such contractual requirements and duties entered into with a customer.
- NGK will strive to continuously review and revise the activities noted herein.
Promotion Framework
To ensure a consistent level of information security across the Group, the NGK Group has established the NGK Group IT Security Standards and updates them every year. By sharing these standards with each Group company, we maintain and improve IT security levels across the Group.
Each Group company prepares action plans for the enactment of countermeasures every year based on these standards and strengthens security in a planned manner. NGK reviews these plans and their implementation status and provides guidance as necessary.
Under normal circumstances, roles and responsibilities for IT security are defined for each division. Risks related to IT security are discussed by the Risk Management Committee and reported to the Board of Directors at least once a year.
To prepare for a security incident affecting a critical system, NGK has established the Cyber Security Countermeasures Headquarters (CSIRT: Computer Security Incident Response Team). Based on the Basic Rules of Crisis Management, this structure enables prompt and appropriate recovery actions.
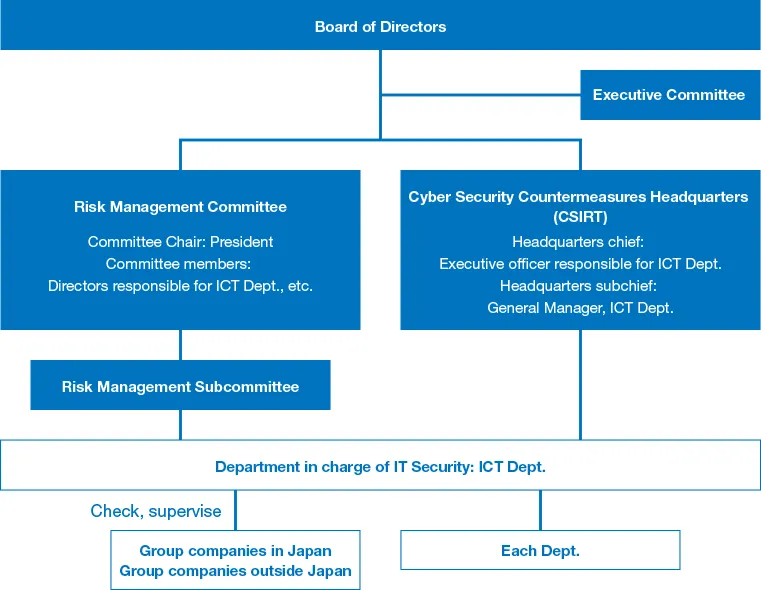
- *When security incidents impacting critical systems occur, our response is based on the Basic Rules of Crisis Management
Strategy, Metrics and Targets
The NGK Group positions information security as a critical management foundation that supports business continuity and public trust. We recognize cyberattacks, information leaks, and other related threats as one of our key management risks, and under a unified Group-wide management framework, we promote measures aimed at preventing incidents and minimizing their impact if they occur.
To assess the effectiveness of our information security measures and drive continuous improvement, we monitor the number of significant security incidents as a KPI. Our target is zero significant security incidents, and no such incidents occurred in FY2025.
We believe this reflects the effectiveness of our management framework based on the Group-wide IT security standards, along with our ongoing employee education and training and awareness-building initiatives such as incident response training and email spoofing training.
At the same time, cyberattacks are becoming more advanced and sophisticated each year, and potential risks remain. We will continue to place the highest priority on preventing incidents, while reviewing training content and management processes and strengthening response capabilities across the Group, with the aim of maintaining our target of zero significant security incidents.
Initiatives
Information Security Measures
The NGK Group manages its information assets appropriately under its Basic NGK Group Information Security Policy, with the General Affairs Department, ICT Department, and other relevant departments working together to support these efforts.
We provide all employees with the Electronic Information Security Handbook and instruct them on its proper use. Employees are also required to report the loss of a personal computer, a computer virus infection, or similar incidents to the General Affairs Department or ICT Department. If confidential information is leaked or an incident has a significant impact on the Company, the employee will be subject to disciplinary action under the rules of employment.
In addition, personnel from the ICT Department visit Group companies every year to check the status of IT security measures and provide guidance. In FY2025, they visited Group companies with shortages of IT personnel and supported risk assessments. We also held IT Global Meetings twice a year for overseas Group companies in North and Central America, Europe, China, and Asia Pacific, with participants joining online, to discuss security operations and raise awareness of incident response measures.
IT Security Training
We conduct training throughout the year to ensure that every employee thoroughly understands IT security. Training for newly hired employees, newly promoted supervisors, and newly promoted managers is provided to NGK employees. We also offer e-learning to NGK employees and employees of some Group companies in Japan.
| Item | Participants | Participation rate |
|---|---|---|
| Training for newly hired employees | 158 | 100% |
| Training for newly promoted supervisors | 243 | 100% |
| Training for newly promoted managers | 99 | 100% |
| E-learning | 8,027 | 98.4% |
- *Excluding employees who were away on maternity leave, childcare leave, long-term business trips, etc
Ensure IT Security Against Cyberattacks
NGK is strengthening the categories of protection, detection, response, and recovery in line with the cybersecurity framework issued by the National Institute of Standards and Technology (NIST) of the United States, and is advancing its preparedness against cyberattacks.
In FY2025, NGK conducted Cyber Security Countermeasures Headquarters drills, as well as email spoofing training for all employees of NGK and its Group companies in Japan, to raise awareness of cyber threats and strengthen security awareness.
No security incidents occurred across the NGK Group in FY2025 that affected business activities.